AI Exposes Major Flaw in Programming Language! Government Websites Shut Down in Several Countries Amid Cyber Attack Fears, Impact Felt in India Too
New Delhi: Artificial Intelligence (AI) has uncovered a massive, decade-old security flaw in PHP, one of the world's most widely used web programming languages. The critical vulnerability—dubbed PHP2Shell—allows cybercriminals to bypass authentication completely and gain unauthorized access to web servers without needing a password.
The revelation has sent shockwaves across the global tech landscape, forcing governments and organizations around the world to temporarily shut down official websites as a precautionary measure.
70% of the Web at Risk
Nearly 70% of all websites on the internet run on PHP technology. Originally created in the early 1990s as Personal Home Page, the language evolved into Hypertext Preprocessor and serves as the core engine powering major platforms like WordPress, Drupal, and Joomla.
Because the vulnerability lies in PHP’s core memory-handling engine rather than individual web applications, virtually every server processing web requests on older or unpatched versions is exposed.
How AI Uncovered the Bug
The vulnerability was identified using advanced AI capabilities:
AI Models Involved: Cybersecurity firm Wiz utilized its platform alongside Google’s Gemini 4 Argon and OpenAI’s GPT-5.6 Sol to discover the flaws.
Unprecedented Speed: Wiz revealed that AI automated and accelerated the tedious process of refining exploits across multiple PHP configurations—completing in a single week what would historically take a full team of security researchers months to accomplish.
OpenAI noted that a design flaw of this magnitude in foundational web architecture has rarely been seen in recent times.
Global Emergency & Government Shutdowns
Amid fears that hacker groups and state-sponsored actors could rapidly weaponize the flaw for remote code execution, distributed denial-of-service (DDoS) attacks, or cryptocurrency mining, nations responded swiftly:
Europe: Ministries of Home Affairs in France, the Netherlands, and Belgium issued emergency directives urging authorities to take vulnerable portals offline immediately.
Global Precautionary Actions: Government portals in several countries, including Finland and Australia, temporarily went offline or restricted access while patches were deployed.
Financial & Media Sector Disruptions: Operations at major banking institutions, financial firms, and digital media portals faced temporary downtime worldwide.
Impact in India & Advisory Issued
The fallout has also reached India. Several Indian organizations and service providers proactively pulled their web services offline to inspect code bases and apply updates.
US Agencies Intervention: The US National Security Agency (NSA), the FBI, and the White House released urgent directives advising all institutions to install the updated PHP patches immediately.
Patch Information: The PHP Foundation released emergency updates (versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35) fixing the flaw. Systems unable to update right away have been strictly advised to remain offline until mitigation measures or web application firewalls (WAF) are deployed.
Related Articles
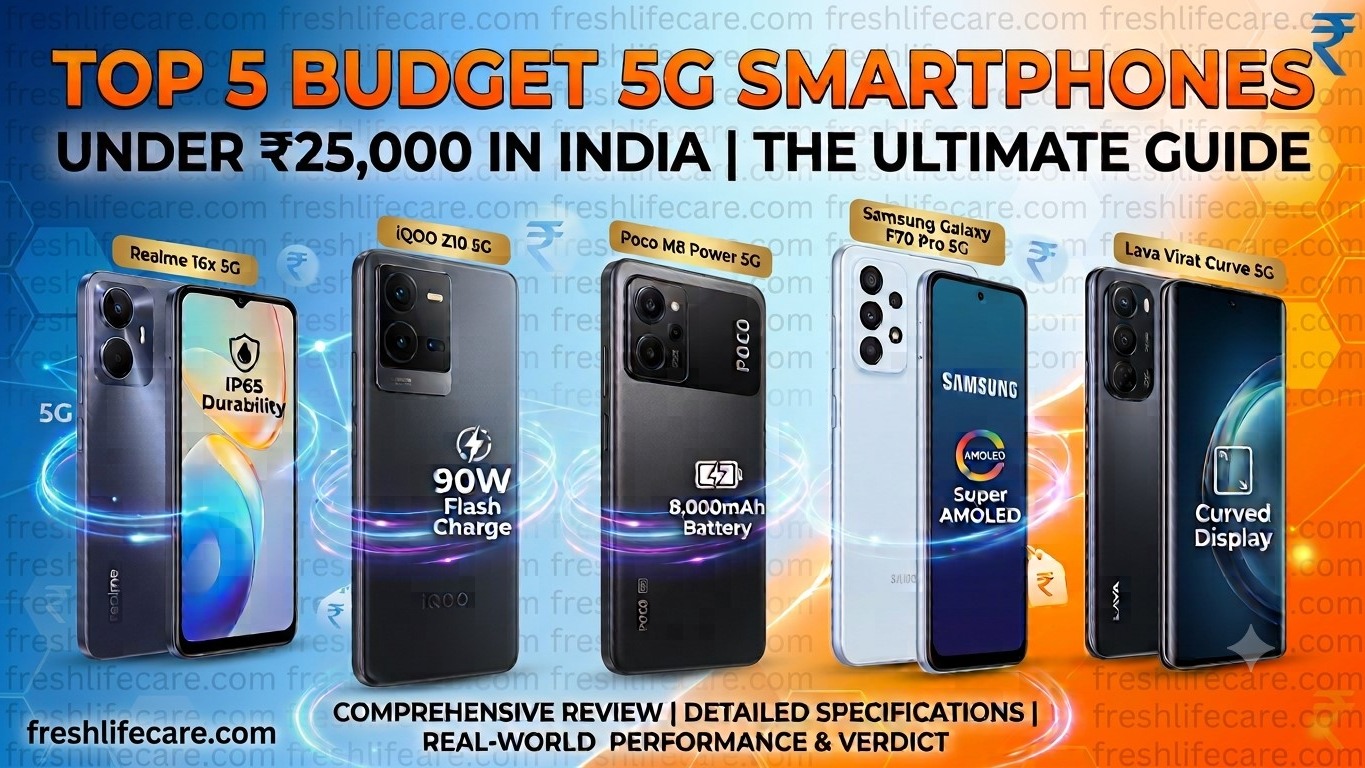
Top 5 Budget 5G Smartphones in India: The Ultimate Buying Guide
Looking for the best 5G phone under ₹25,000 in India? Explore our top 5 picks featuring massive batteries, fast charging, AMOLED screens, and performance reviews.
Read More
In India 23% Price Hike in One Year: ACs, TVs, and Fridges Set to Get Costlier from October 1
AC, TV, and refrigerator prices are set to increase again from Oct 1. Read about the 23% annual price hike and how long existing stocks will last.
Read More
The AI Search Backlash: Why Users and Publishers Want the Google’s Old Search Engine Back
Explore the growing Google AI search backlash. This infographic illustrates why users are frustrated and publishers face traffic decline due to AI Overviews. Discover why they want the old Google back.
Read More